DEVELOPER GUIDEHow to verify a WhatsApp webhook signature
A practical boundary for authenticating webhook events before your application parses or acts on them.
Developer guide for webhook signature verification. Validate the behavior in your own stack before production rollout.The problem
Capture the raw request bytes and the signature header. Compute the expected HMAC with your server-side secret.
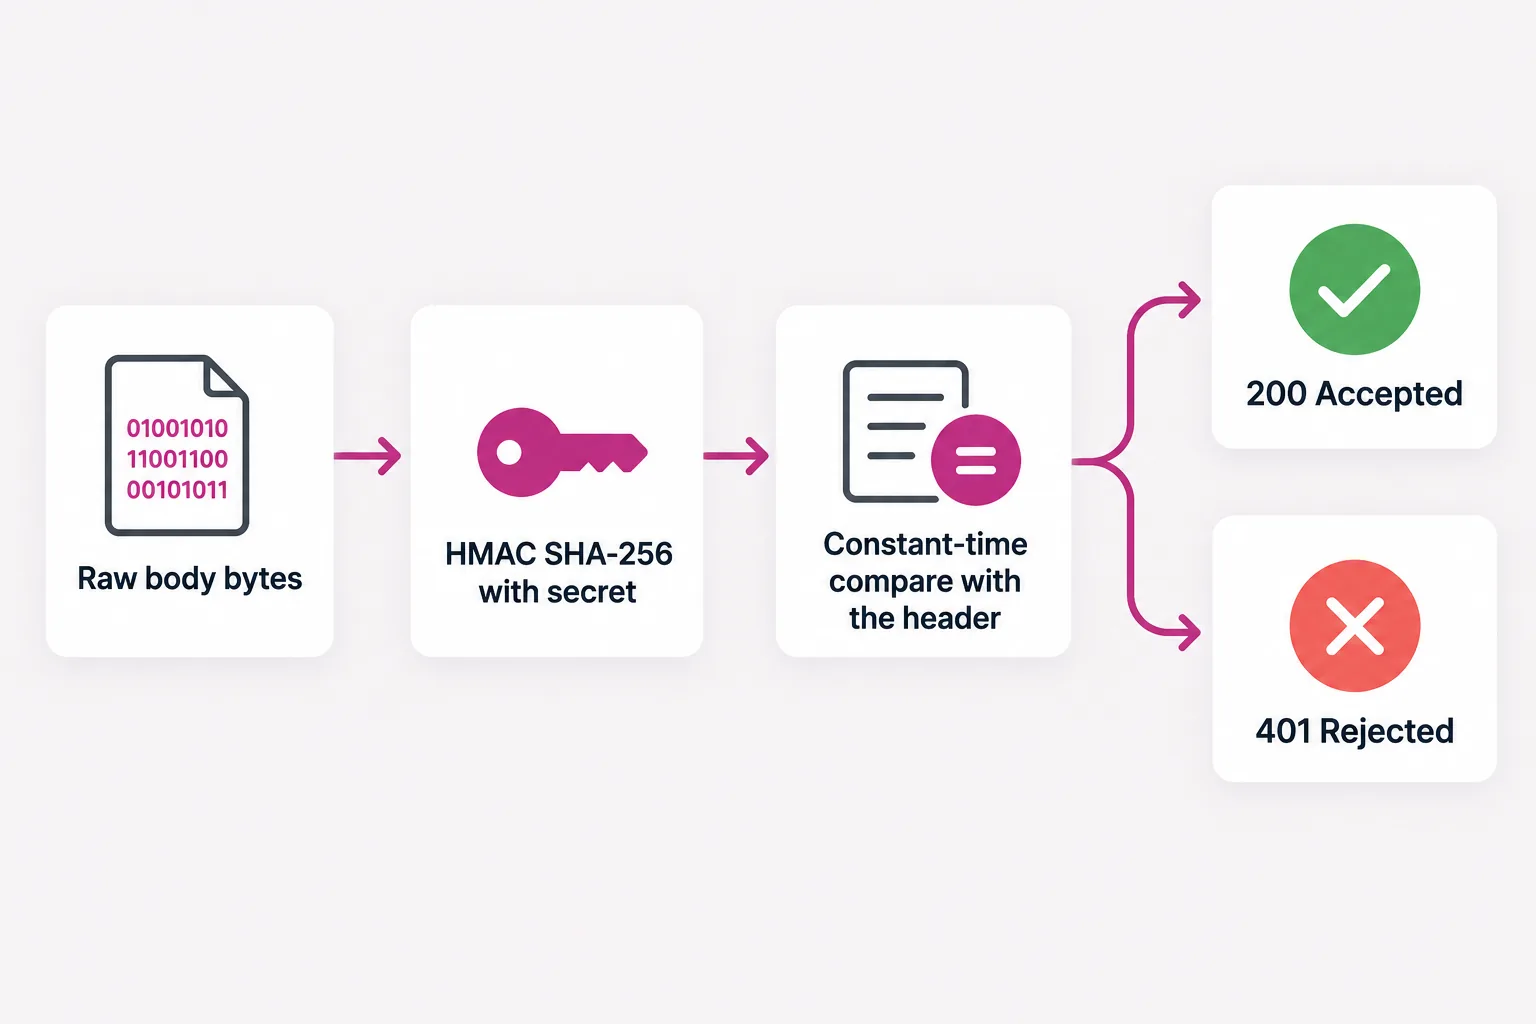 Verify the raw bytes before parsing anything.
Design the boundary
Compare fixed-length values in constant time, reject stale timestamps and return 401 before parsing untrusted data.
Process the interaction
Persist the event only after verification, then acknowledge and queue downstream work.
Measure the outcome
Test malformed headers, stale timestamps, body mutations and secret rotation.
BUILD IT SAFELYMake the failure path part of the design.
Reliable messaging is an operational system, not only an API call.
Start free 